Bill · S. 1851· Senate(119-S-1851)
Healthcare Cybersecurity Act of 2025
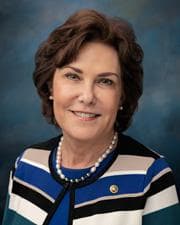
- Introduced
- 5/21/2025
- Last activity
- 5/21/2025 — Read twice and referred to the Committee on Homeland Security and Governmental Affairs.
- Sponsored by
- Jacky Rosen
- Cosponsors
- - 0 - 2
- Introduced
- In Committee
What this bill would do
The Healthcare Cybersecurity Act of 2025 aims to strengthen the cybersecurity of the Healthcare and Public Health Sector. It requires the Cybersecurity and Infrastructure Security Agency to coordinate closely with the Department of Health and Human Services. This includes appointing a liaison to facilitate information sharing and help implement a specific Risk Management Plan. The bill mandates training for healthcare owners and operators regarding cyber risks and mitigation. It also allows for the identification and listing of high-risk covered assets to prioritize resource allocation. Finally, the Act requires various reports to Congress to ensure accountability and transparency.
Yes· 3 of 12
Does this better protect the country from computer attacks?+7
The bill directly enhances the cybersecurity of the critical healthcare and public health infrastructure.
Does this give people more control over their personal data?+5
The bill aims to protect sensitive patient health information and electronic health records from cyberattacks.
Does this protect people from being watched or searched?+4
Enhanced cybersecurity directly improves the privacy of sensitive health data.
The opposite
No question was scored the opposite.
Who it would affect, and how
Potential Positive Impacts for People
-
Improved Cybersecurity Training: The Agency will provide training to owners and operators of covered assets regarding cybersecurity risks and ways to mitigate those risks (Section 5).
-
Enhanced Resource Allocation: The Secretary can develop a list of high-risk covered assets to help the Department prioritize where to send resources to strengthen cyber resilience (Section 7(b)(4)).
-
Increased Coordination and Information Sharing: A designated liaison will help facilitate the sharing of cyber threat information between the Department and the Agency (Section 4(b)(2)(C)).
-
Targeted Support for Vulnerable Assets: The Risk Management Plan will include an analysis of how risks impact rural and small- or medium-sized covered assets (Section 6(a)(1)).
-
Addressing Workforce Shortages: The Plan includes an assessment of cybersecurity workforce shortages, including issues with training, recruitment, and retention (Section 6(a)(4)).
Potential Negative Impacts for People
-
Potential Designation as High-Risk: The Secretary has the authority to determine if a covered asset is "high-risk" and notify the owners and operators of that designation (Section 7(b)(1)).
-
No New Funding Authorized: The Act explicitly states that no additional funds are authorized to be appropriated for the purpose of carrying out this Act (Section 9(c)).
Groups and Interests Ranking
Every group the model scored this bill for, from -10 to +10. Hover a score for the reason it gave.
- Governance And Ideology
- Improves Privacy Rights+4Improves Government Transparency+3Increases Federal Power+2
- National Security And Foreign Policy
- Improves Cybersecurity Defense+7
- Economy And Finance
- Improves Consumer Protection+3Improves Small Business Support+2
- Education And Technology
- Improves Data Privacy+5
- Demographic And Interest Groups
- Good For Business Owners+2Good For Rural Residents+2
- Healthcare
- Improves Healthcare Access+2Reduces Hospital Costs+1
- Environment Energy And Infrastructure
- Improves Rural Development+2
- 6/2/2025
- 2 Cosponsors added.
- 5/21/2025
- Read twice and referred to the Committee on Homeland Security and Governmental Affairs.
- 1 Cosponsor added.
- Introduced in Senate
One bill Congress.gov lists as related to this one — companions in the other chamber, earlier versions, and bills this one absorbed or was folded into.
 Angus King
Independent · Maine
 Thomas Tillis
Republican · North Carolina
 Todd Young
Republican · Indiana