Bill · H.R. 4126· House(119-HR-4126)
ARMS Act
- Introduced
- 6/25/2025
- Last activity
- 6/26/2025 — Referred to the Subcommittee on Transportation and Maritime Security.
- Sponsored by
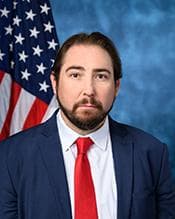
- Elijah Crane
- Cosponsors
- - 1 - 0
- Introduced
- In Committee
What this bill would do
The Aviation Risk Mitigation and Security Act directs the TSA to establish a system for conducting covert testing of aviation security operations. This includes project scenarios focused on airport passenger and baggage screening to identify vulnerabilities. The TSA must implement a long-term testing program based on annual risk assessments of emerging threats. The bill also requires the TSA to establish a process for analyzing and mitigating any identified security vulnerabilities. Furthermore, the TSA is required to produce annual reports regarding these testing results and mitigation efforts.
Yes· 3 of 4
Does this make what the government does easier for the public to see?+5
The bill requires the TSA to publish summary performance data for Category X airports on a publicly accessible website.
Would people in cities be better off under this?+1
While the bill affects all airports, the mandate specifically targets Category X airports which are often located near major urban centers.
Does this improve buses, trains and other public transport?+1
The bill enhances aviation security, which is a critical component of the national transportation infrastructure.
The opposite
No question was scored the opposite.
Who it would affect, and how
Potential Positive Impacts for People
-
Strengthened Aviation Security: The TSA will establish a system for conducting risk-informed, headquarters-based covert testing to identify and assess vulnerabilities in passenger and baggage security screening operations (Section 2(a)(1)).
-
Proactive Threat Response: The bill requires a long-term program that uses annual risk assessments of emerging threats to evaluate the effectiveness of security operations (Section 2(a)(2)).
-
Accountability via Root Cause Analysis: If a vulnerability is found, the TSA must conduct a root cause analysis within 90 days to determine the origin of the issue (Section 2(c)(2)).
-
Verification of Security Improvements: The TSA must conduct retesting within 180 days after mitigation measures are completed to ensure the new measures actually work (Section 2(c)(4)).
-
Public Transparency: The TSA must publish a summary of performance data on a publicly accessible website, including aggregate pass and failure rates for tests conducted at Category X airports (Section 2(d)(3)(A)).
Potential Negative Impacts for People
- No specific negative impacts or burdens are explicitly stated in the provided text.
Groups and Interests Ranking
Every group the model scored this bill for, from -10 to +10. Hover a score for the reason it gave.
- Governance And Ideology
- Improves Government Transparency+5
- Demographic And Interest Groups
- Good For Urban Residents+1
- Environment Energy And Infrastructure
- Improves Public Transit+1
- National Security And Foreign Policy
- Improves Cybersecurity Defense+1
- 7/15/2025
- 1 Cosponsor added.
- 6/26/2025
- Referred to the Subcommittee on Transportation and Maritime Security.
- 6/25/2025
- Referred to the House Committee on Homeland Security.
- Introduced in House
 Brandon Gill
Republican · Texas